SIEM and Security Incident Management Integration
We unify log collection, correlation, alerting and response workflows in a SIEM-centered SOC operating model.

Operational Outcomes You Gain
We improve incident visibility and reduce end-to-end response time.
Events from multiple log sources are correlated in one SIEM layer.
Critical alerts are scored by business impact and actioned earlier.
Lifecycle status and KPI trends become traceable for governance.
How We Work
SIEM integration is delivered through source onboarding, correlation design, playbooks and KPI tuning.
Firewall, EDR, server, application and cloud sources are inventoried.
Use-case driven rules and escalation tiers are designed.
Ticketing, runbooks and ownership flows are linked with SIEM alerts.
MTTD, MTTR and alert quality metrics drive recurring optimization.
SIEM and Incident Metrics
We measure success through detection speed, response time and alert quality.
Correlation rules reduce mean time to detect critical threats.
Playbook-driven workflows lower mean time to respond.
False positives are reduced to improve analyst efficiency.
Incident and response trends are reviewed with regular KPI reports.
Frequently Asked Questions
Usually no. Existing log sources can be onboarded in phased integration waves.
Firewall, EDR, AD, server, application, cloud and network device logs can be onboarded.
Yes. Alerts can be mapped to ticket workflows with ownership automation.
Yes. We provide KPI-driven summaries for both technical and executive audiences.
Related Security Services
Complete SIEM operations with procurement, endpoint security and network defense services.
Strengthen Your SIEM and Incident Workflow
Improve detection and response capabilities with measurable KPI-driven governance.
Posts Related to This Service
Explore technical guides and decision-support content connected to this solution.
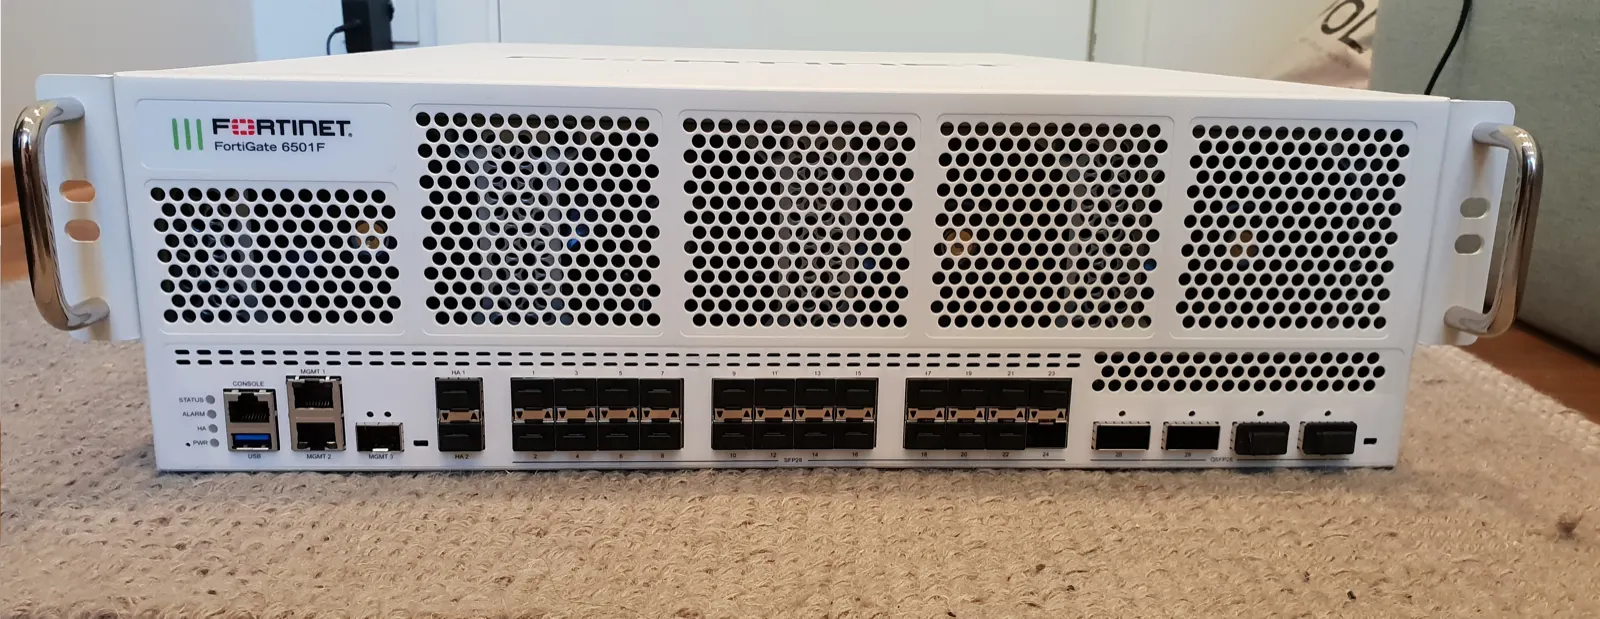
How to Achieve ISO 27001 Network Security with FortiGate (2026)
Use FortiGate for ISO 27001 network security: segmentation, firewall policy, VPN, logging, admin hardening, and SoA evidence—with a practical checklist.
Read Article
KVKK-Compliant Network Security with FortiGate (2026 Guide)
How to use FortiGate for KVKK-aligned network security: segmentation, access control, VPN, logging, encryption balance, and a practical technical-controls checklist.
Read Article
ISO 27001 and Network Security: Firewall and VPN Requirements
We examine network security, firewall management, and VPN requirements within the scope of ISO 27001 Information Security Management System (ISMS) Annex A technological controls.
Read Article